


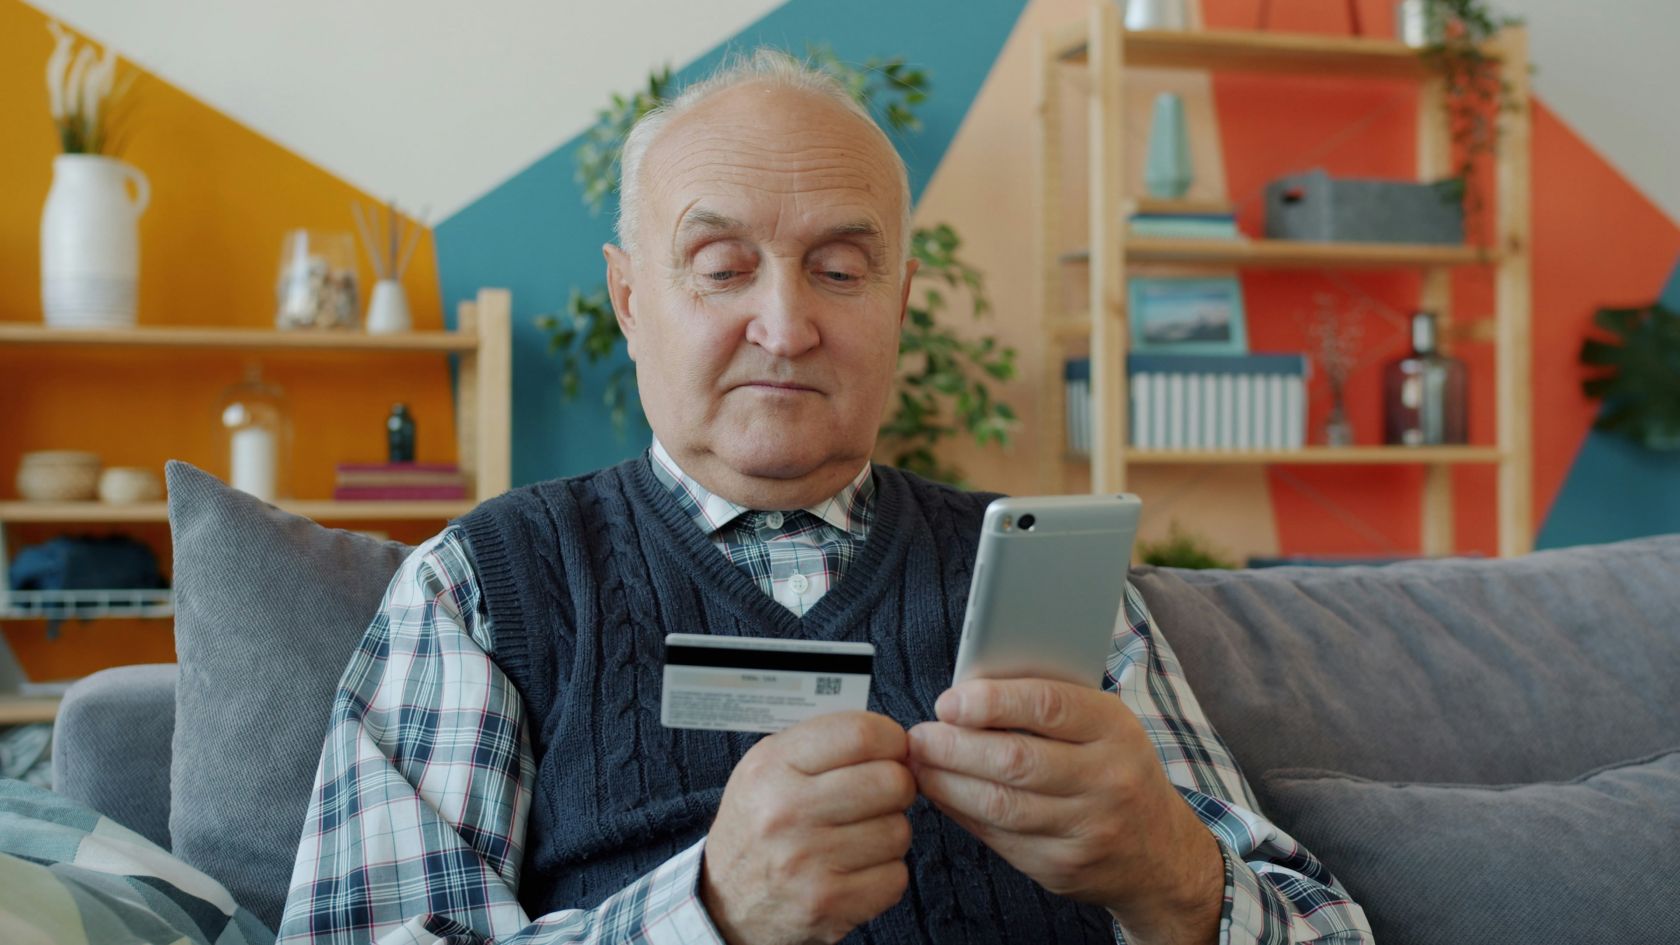
The warning concerns a smishing scheme using spoofing, a technique that disguises the true origin of a message or call so that the displayed name or number appears legitimate, Postal reports.
Fraudsters may send an email or SMS containing a link to a website designed to imitate the bank’s website. Victims are then asked to provide login credentials or other personal information.
After obtaining this information, scammers may also call from a number appearing to belong to Caixa and request banking credentials or security codes, claiming they are needed to cancel fraudulent transactions.
Caixa warns customers against sharing codes
CGD says it does not send SMS messages or emails containing links to warn customers about suspicious activity.
The bank also does not request SMS Token codes, matrix card details, personal information or Caixadirecta credentials by SMS or email, nor does it ask customers to use an ATM to cancel suspected fraud.
Customers should not click links or provide information in response to suspicious messages or calls. Anyone who suspects they have been targeted should contact CGD and the authorities.
Set The Portugal News as your preferred source for news on Google
 Add as a preferred source on Google







 Portugal Handbook
 English
 Nederlands
 Deutsch
 Français
 Español
 Italiano
 Svenska
 Pусский
 中文
 Türkçe
 Português
 Czech
 Hungarian
 Polski
 عربي
 Suomi
 עִברִית
 Português (Brasil)

Follow us on social media